Learning path
Administrator
Set up your department, organize people and units, and understand how settings affect daily work.
 Academy
The Resgrid learning center
Practical video walkthroughs and guides for the people who dispatch, respond, and run the department. Find the right tools, understand your settings, and learn at your own pace.
Start with your role
Focus on the workflows and decisions that matter to your day.
Learning path
Set up your department, organize people and units, and understand how settings affect daily work.
Learning path
Coordinate calls, find available resources, and follow communications and response status.
Learning path
Use your apps, update availability, follow shifts, and complete assigned learning and checks.
Learning path
Manage equipment, inventory, records, deployments and supporting department workflows.
Learn the apps. Follow the workflow.
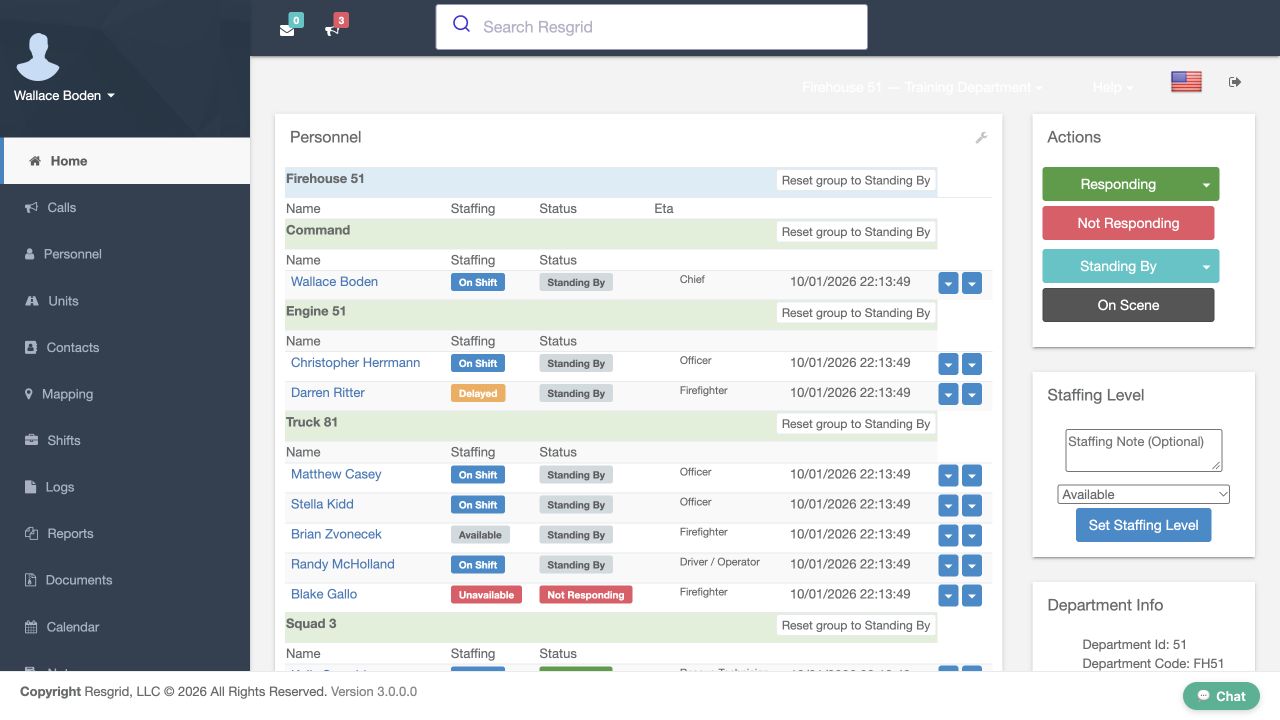
Follow real Resgrid screens and practice the workflows with examples for your department.
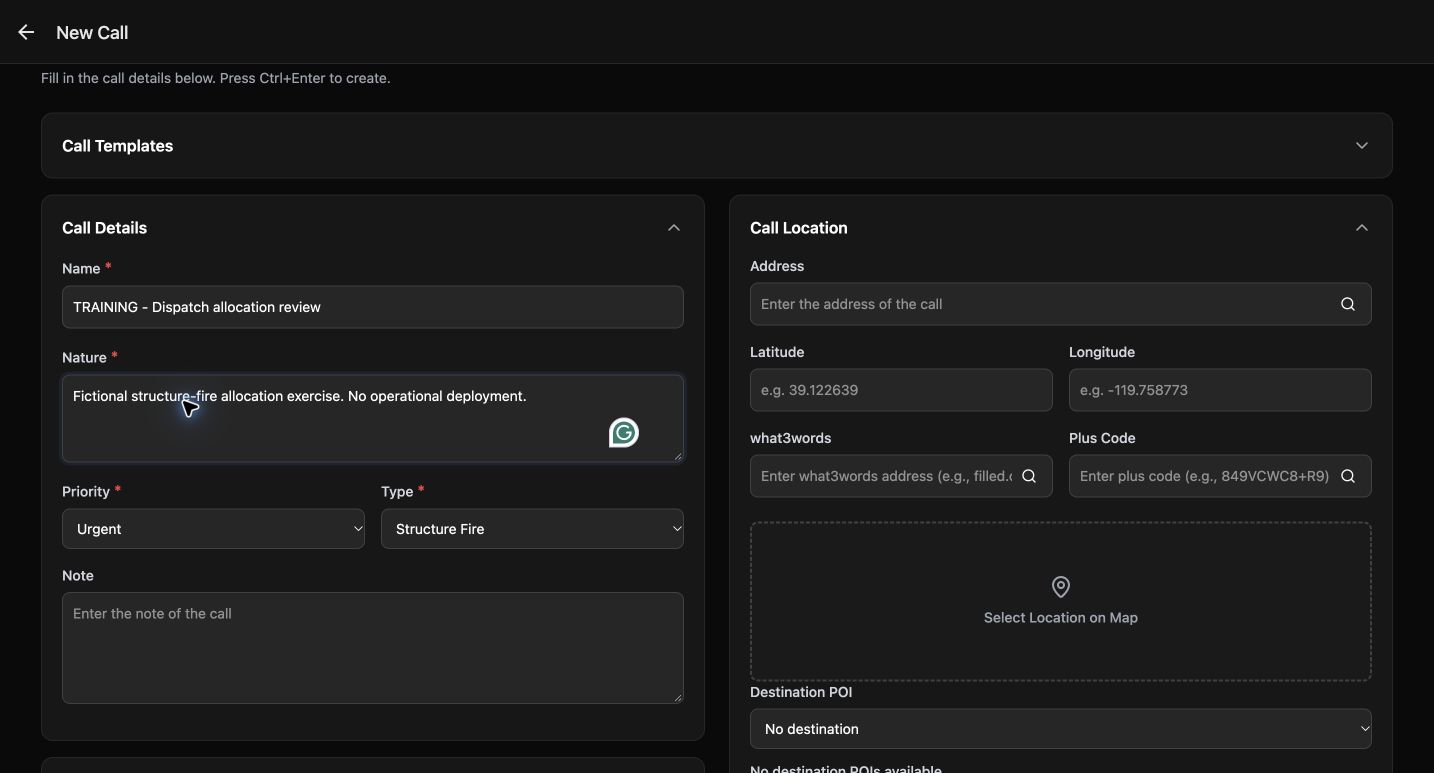
Dispatch · Video walkthrough
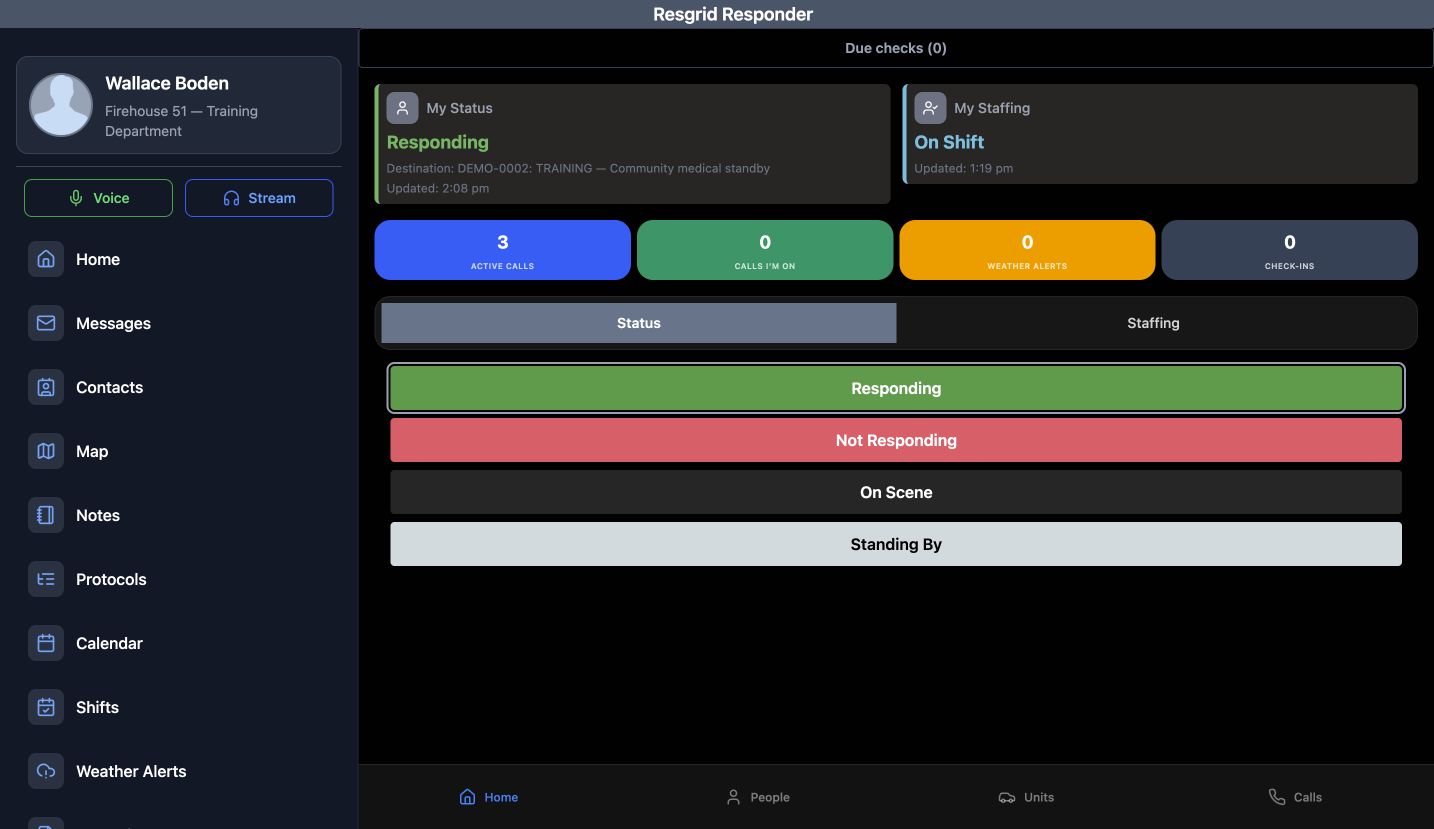
Responder · Video walkthrough
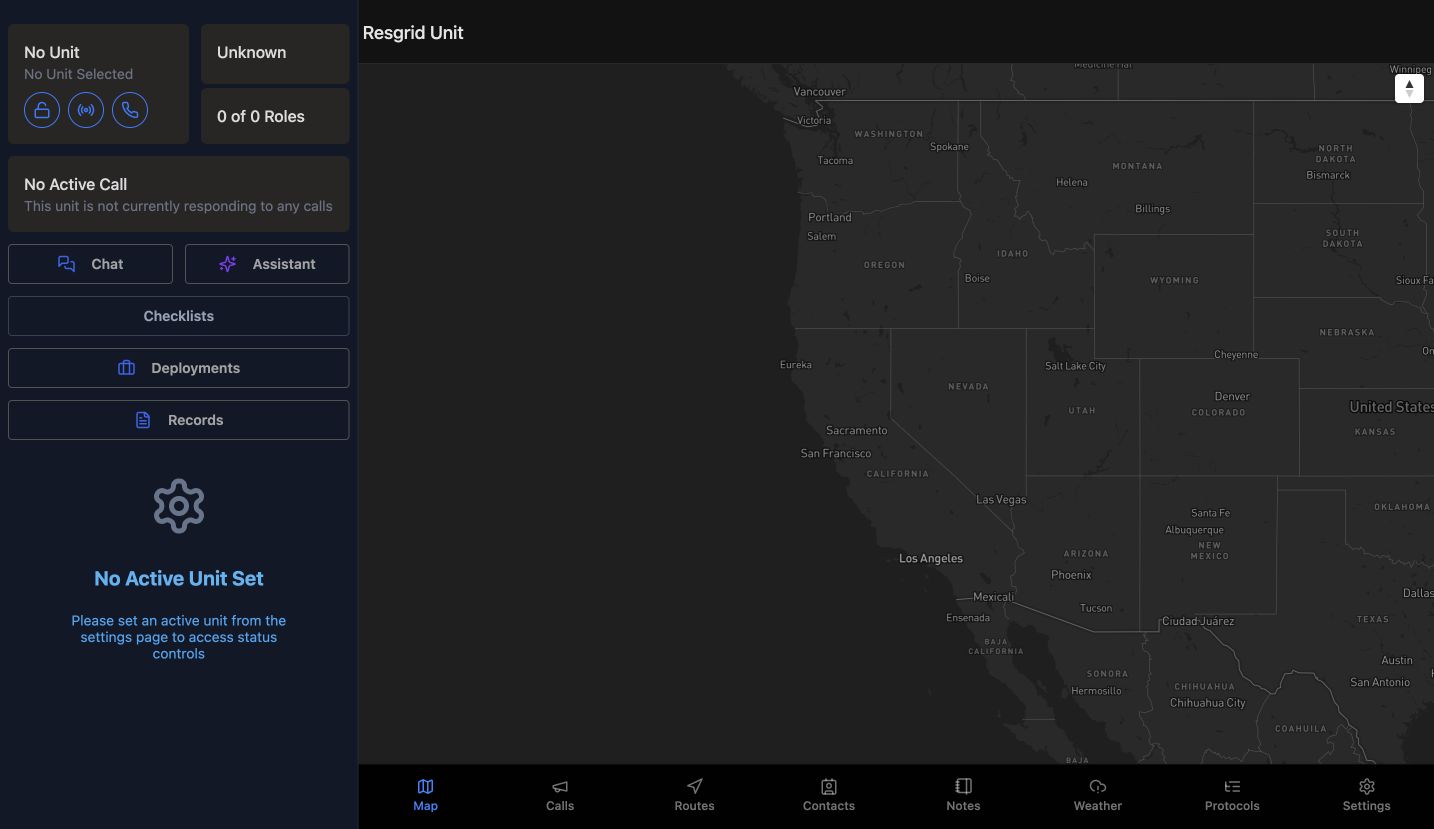
Unit · Video walkthrough
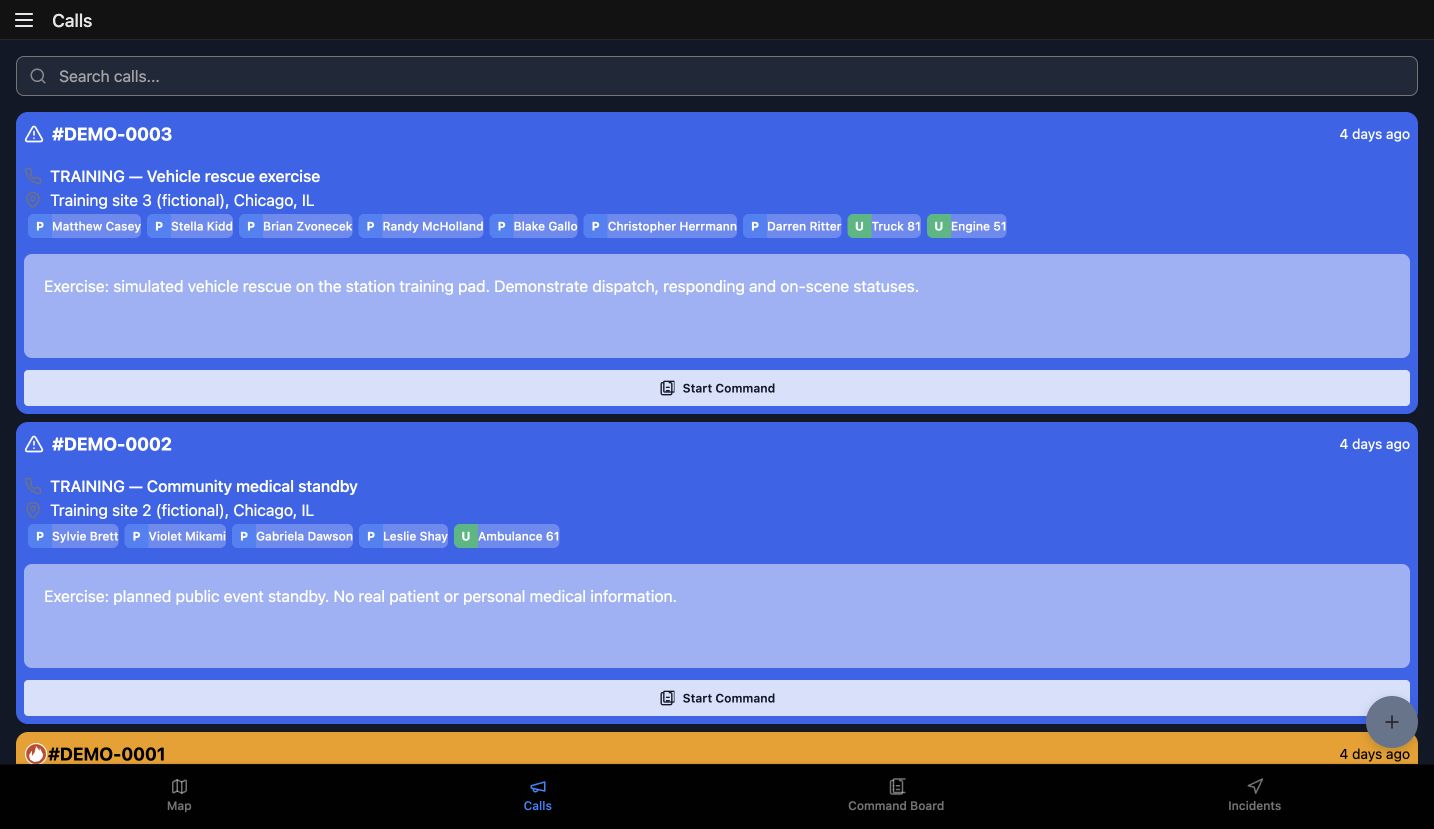
IC · Video walkthrough
Explore the system
Read the purpose, setup decisions and practical use of each area.
Topic guide · orientation
Topic guide · people
Topic guide · security
Topic guide · units
Topic guide · apps
Topic guide · calls
Topic guide · communication
Topic guide · mapping
Topic guide · shifts
Topic guide · training
Topic guide · knowledge
Topic guide · checklists
Topic guide · maintenance
Topic guide · inventory
Topic guide · records
Topic guide · deployments
Topic guide · business
Topic guide · automation
Topic guide · ptt
Topic guide · adp
Topic guide · plans
Topic guide · ai
Topic guide · relay
Topic guide · self hosting
Topic guide
All department roles
Welcome to Resgrid Academy. Resgrid brings dispatch, people, apparatus, and department management into a connected system. This series explains what each feature does, how to prepare it, and how to tell whether it is helping your department.
Picture a fictional department with two stations, an engine, and a rescue unit. First, administrators organize members, groups, roles, and units. A dispatcher creates a training call and selects the intended resources. Members respond through their assigned devices. After closeout, officers complete records and follow up on equipment, supplies, and staffing.
Start with the foundation. Set the department address and time zone. Build the roster, home stations, personnel roles, and unit types. Review who can dispatch, manage information, and administer the department. Prepare account recovery as you set up stronger sign-in protections. These choices influence later schedules, recipients, maps, and reports.
For operations, learn call intake, types, priorities, recipient routing, run cards, and response statuses. Mapping adds location and site context. Messaging and notification rules keep the intended audience informed. Verify communications on actual devices. A saved call or provider handoff is different from confirmed receipt by a member.
Between calls, shifts help plan coverage. Training and certification records make learning and renewal work visible. Checklists record routine inspections. Maintenance gives defects an owner and a documented repair process. Inventory records where equipment and supplies are stored, issued, and replenished. Documents, contacts, protocols, and calendars give members a shared reference point.
Records connect incident reporting, prevention, investigation, evidence, review, and disclosure. Deployments keep extended response activity and supporting documents together. Business Operations adds commercial and costing workflows where enabled. Teach the source activity, review decisions, and recorded outcomes together, rather than treating an export or prepared claim as a completed external submission.
Feature availability depends on the deployed release and department access. Some features need an enabled module, a permission, an add-on, or protection enrollment. The source catalog marks Enhanced AI as planned. Buying an add-on is separate from configuring it. Setup Report helps review configuration evidence; it does not prove that every operational workflow or notification has succeeded.
Choose the learning path that matches your responsibility: administrator, dispatcher, member, or specialist. Each chapter explains a department problem, the relevant features, setup decisions, and a practice task.
See the steps in Resgrid
Follow actual Resgrid screens through configuration and daily workflows using a fictional department. Videos include captions, chapters and downloads.
Watch the walkthroughs → Follow a connected department workflowFind the right tool
Understand what a feature does, which problem it solves and how to prepare it.
Member accounts, contact details and status.
Dispatch, notifications, permissions and reports all start from who belongs to which group, so set this up first.
Invite members or add them directly, then check that each has a mobile number or email address.
Email invitations for new members to join the department.
Dispatch, notifications, permissions and reports all start from who belongs to which group, so set this up first.
Send invitations and follow up on any that have not been accepted.
Stations and groups that organize members and units.
Dispatch, notifications, permissions and reports all start from who belongs to which group, so set this up first.
Create a station group for each station with its address, and organizational groups for teams, then add members.
Roles such as Firefighter, EMT or Officer.
Describe responsibility consistently without assuming that a role proves qualification.
Create the roles you dispatch or report on, and assign them to members.
Create a member account directly instead of sending an invitation.
Dispatch, notifications, permissions and reports all start from who belongs to which group, so set this up first.
Have your member list with email addresses or mobile numbers, and decide how stations or teams are grouped.
Create a station or group.
Dispatch, notifications, permissions and reports all start from who belongs to which group, so set this up first.
Have your member list with email addresses or mobile numbers, and decide how stations or teams are grouped.
Department address, time zone and core settings.
Sets the time zone and address everything else uses, and keeps administrative access limited and recoverable.
Confirm the address and time zone; dates, maps and schedules depend on them.
Turn optional modules on or off for the department.
Reduce navigation clutter while understanding retained data and add-on prerequisites.
Hide modules you will not use so members see a simpler menu.
Who can create calls, see personal information and perform other sensitive actions.
Review who can perform sensitive work and which resources they may see.
Review each permission; some default to every member.
Two-factor sign-in for member accounts.
Sets the time zone and address everything else uses, and keeps administrative access limited and recoverable.
Enroll every administrator in two-factor sign-in.
Two-factor requirements, password rules and session limits.
Review lockout and recovery risks with an enrolled administrator.
Require two-factor sign-in for administrators and review password and session rules.
Let members sign in through your identity provider, with optional automatic account provisioning.
Review identity mapping, local fallback and recovery before enforcing SSO.
Know your department address and time zone, and choose at least two people who will administer Resgrid.
See who changed department settings and when.
Identify what changed and who should verify the effect.
Know your department address and time zone, and choose at least two people who will administer Resgrid.
Your own sign-in sessions, password and two-factor settings.
Keep personal account recovery distinct from department-wide settings.
Know your department address and time zone, and choose at least two people who will administer Resgrid.
Setup Wizard, Setup Report and Admin Assist.
Keep learning, configuration and verification as separate steps.
Know your department address and time zone, and choose at least two people who will administer Resgrid.
Your apparatus, vehicles and response teams.
Units let dispatchers send the right resources and let everyone see which apparatus is available.
Add each unit with its type and home station group.
Categories such as Engine, Ladder or Ambulance.
Group comparable resources without assuming staffing or qualification.
Create unit types before adding units so each unit can be classified.
GPS devices that report unit locations.
Review device ownership, stale-position behavior and fallback sources.
Register each tracking device and link it to its unit.
Add an apparatus, vehicle or team.
Units let dispatchers send the right resources and let everyone see which apparatus is available.
List your apparatus or response teams with their types and home stations. Teams that respond only as individuals can mark this module not applicable.
Assign crew members to units.
Units let dispatchers send the right resources and let everyone see which apparatus is available.
List your apparatus or response teams with their types and home stations. Teams that respond only as individuals can mark this module not applicable.
The member app for receiving dispatches, responding and setting status.
Separate member device setup from department configuration and verify each member's channels.
Have every member install the Responder app, sign in and allow notifications.
The in-vehicle app that represents an apparatus.
Review device identity, assigned crew and unit communications together.
Install the Unit app on each apparatus tablet and select its unit.
The dispatcher view for creating and managing calls.
Give dispatch personnel a focused operating surface alongside web administration.
Give dispatch access to the people who dispatch, then have them sign in.
Before you begin: Dispatch App Login permission
Incident command and accountability for incident commanders.
Prepare command structures and access before an exercise or response.
Give command access to the officers who run incidents.
Before you begin: Command App Login permission
A station display of calls, units and personnel.
Choose display refresh, location age and visibility appropriate to a station screen.
Open the Big Board on a station screen and choose what it shows.
The department home page: current status, staffing and activity.
Most members use Resgrid through the Responder app. Getting everyone installed and signed in is what lets dispatches reach them.
Decide which devices each role will use and share the app download links with your members.
Your own profile, contact details and notification preferences.
Most members use Resgrid through the Responder app. Getting everyone installed and signed in is what lets dispatches reach them.
Decide which devices each role will use and share the app download links with your members.
Switch between the departments you belong to.
Most members use Resgrid through the Responder app. Getting everyone installed and signed in is what lets dispatches reach them.
Decide which devices each role will use and share the app download links with your members.
The call types and priorities used to classify calls.
Use consistent reporting and run-card matching terms.
Add the call types your dispatchers use and set their priorities.
The statuses members and units report, such as Responding or On Scene.
Use terminology familiar to the department while preserving automation meaning.
Review the built-in statuses and add your own where your terms differ.
How calls page personnel: by group or by shift, and related automatic status changes.
Consistent call types and statuses make dispatching, response tracking and reporting reliable from the first call.
Choose whether dispatch follows groups or shifts, and review the automatic status options.
Create calls automatically from CAD, paging or email dispatches.
Review parsing, routing and observed integration failures before activation.
Choose your CAD or paging format and connect the mailbox that receives dispatches.
Recommended resources for each call type or area.
Review candidate coverage before enabling operational use.
Build run cards for your most common calls, then turn on recommendations.
Before you begin: Feature access enabled by your system operator
Active calls and their dispatch status.
Consistent call types and statuses make dispatching, response tracking and reporting reliable from the first call.
Collect your call types, the statuses members report while responding, and the details of any CAD or paging system that should create calls.
Create and dispatch a call.
Consistent call types and statuses make dispatching, response tracking and reporting reliable from the first call.
Collect your call types, the statuses members report while responding, and the details of any CAD or paging system that should create calls.
Closed and past calls.
Consistent call types and statuses make dispatching, response tracking and reporting reliable from the first call.
Collect your call types, the statuses members report while responding, and the details of any CAD or paging system that should create calls.
Reusable call text and note templates that speed up call entry.
Reduce repeated entry while keeping dispatch decisions explicit.
Collect your call types, the statuses members report while responding, and the details of any CAD or paging system that should create calls.
Timers that remind responders on a call to check in, with escalation when they do not.
Review lone-worker and response follow-up with approved local procedures.
Collect your call types, the statuses members report while responding, and the details of any CAD or paging system that should create calls.
Create calls and accept member commands by text message.
Make approved inbound sources and their operational effects explicit.
Collect your call types, the statuses members report while responding, and the details of any CAD or paging system that should create calls.
The mailbox and format used to import calls from CAD or paging email.
Consistent call types and statuses make dispatching, response tracking and reporting reliable from the first call.
Collect your call types, the statuses members report while responding, and the details of any CAD or paging system that should create calls.
Rules that alert chosen people when calls, statuses or other events happen.
Reduce missed follow-up and review unnecessary message volume.
Create notification rules for the events officers and administrators need to know about.
Reusable recipient lists, including email lists.
Keep audience ownership explicit and review recipients before sending.
Create lists for groups you message often, such as Officers.
Test messages that show whether members can be reached.
Collect observed test evidence; registration alone does not prove delivery.
Run a communication test before going live and after major changes.
Team chat for members.
A dispatch only helps if it reaches people. This is where you confirm members can actually be contacted.
Create channels for your teams once chat is enabled.
Before you begin: Feature access enabled by your system operator
Messages sent to you.
A dispatch only helps if it reaches people. This is where you confirm members can actually be contacted.
Make sure members have added a mobile number or email address and installed the Responder app.
Before you begin: Messaging module enabled
Messages you have sent.
A dispatch only helps if it reaches people. This is where you confirm members can actually be contacted.
Make sure members have added a mobile number or email address and installed the Responder app.
Before you begin: Messaging module enabled
Send a message, poll or callback request to members.
A dispatch only helps if it reaches people. This is where you confirm members can actually be contacted.
Make sure members have added a mobile number or email address and installed the Responder app.
Before you begin: Messaging module enabled
Connect the Resgrid Assistant to chat platforms and choose what it may do.
Keep automated access and confirmations under administrator control.
Make sure members have added a mobile number or email address and installed the Responder app.
The live map of personnel, units and calls.
A current map shows where responders and apparatus are and puts important locations in front of dispatchers.
Set how long locations stay on the map in the mapping settings.
Before you begin: Mapping module enabled
Points of interest such as stations, hospitals and hydrants.
A current map shows where responders and apparatus are and puts important locations in front of dispatchers.
Add the locations dispatchers need to see.
Before you begin: Mapping module enabled
Weather alert zones and alert notifications.
Review alert coverage and automatic-message settings before use.
Draw the zones you cover and choose who is alerted.
Add your own shapes and overlays to the map.
A current map shows where responders and apparatus are and puts important locations in front of dispatchers.
Confirm members allow location sharing in the Responder app, and decide how long a position should stay on the map.
Before you begin: Mapping module enabled
Directions and routes for responding resources.
A current map shows where responders and apparatus are and puts important locations in front of dispatchers.
Confirm members allow location sharing in the Responder app, and decide how long a position should stay on the map.
Before you begin: Mapping module enabled
Upload your own map images, such as a campus or venue map.
Give responders useful reference layers with an identified owner and update process.
Confirm members allow location sharing in the Responder app, and decide how long a position should stay on the map.
Before you begin: Mapping module enabled
Floor plans and zones for buildings.
Keep building references available to authorized users without inferring safe routes.
Confirm members allow location sharing in the Responder app, and decide how long a position should stay on the map.
Before you begin: Mapping module enabled
Planned routes, such as patrols, and who is assigned to them.
Prepare recurring route information with current source ownership.
Confirm members allow location sharing in the Responder app, and decide how long a position should stay on the map.
Before you begin: Mapping module enabled; Manage Routes permission
Shift schedules, sign-ups and trades.
Shifts show who is on duty and can drive dispatch, so calls page the people who are actually working.
Create your shifts, assign groups and members, and decide whether dispatch follows shifts.
Before you begin: Shifts module enabled
The department calendar for meetings, events and training nights.
Shifts show who is on duty and can drive dispatch, so calls page the people who are actually working.
Add recurring meetings and training nights.
Before you begin: Calendar module enabled
Add an event to the department calendar.
Shifts show who is on duty and can drive dispatch, so calls page the people who are actually working.
Have your rotation or duty schedule, and decide whether dispatch should follow shifts.
Before you begin: Calendar module enabled
Repeating work schedules for staff.
Review schedule ownership and local time separately from dispatch eligibility.
Have your rotation or duty schedule, and decide whether dispatch should follow shifts.
Before you begin: Shifts module enabled
Training assignments with materials and optional quizzes.
See who is qualified and whose certifications are expiring before it affects who can respond.
Create a training and assign it to the members or groups who need it.
Before you begin: Training module enabled
The certifications and qualifications you track.
See who is qualified and whose certifications are expiring before it affects who can respond.
Add each certification type with its renewal period.
Who holds which certifications and what is expiring.
See who is qualified and whose certifications are expiring before it affects who can respond.
Record members' current certifications, then review what expires soon.
Create a training, with an optional quiz.
See who is qualified and whose certifications are expiring before it affects who can respond.
List the certifications your department tracks and their renewal periods.
Before you begin: Training module enabled
What happens when a certification expires, grace periods and reminders.
See who is qualified and whose certifications are expiring before it affects who can respond.
List the certifications your department tracks and their renewal periods.
Your own certification records.
See who is qualified and whose certifications are expiring before it affects who can respond.
List the certifications your department tracks and their renewal periods.
Shared contacts such as hospitals, agencies and vendors.
Members find the current procedure, preplan or phone number when they need it instead of searching email.
Add the outside contacts members call most.
Shared documents such as procedures and preplans.
Members find the current procedure, preplan or phone number when they need it instead of searching email.
Upload your most-used documents and organize them by category.
Before you begin: Documents module enabled
Dispatch protocols with scripted questions and instructions.
Members find the current procedure, preplan or phone number when they need it instead of searching email.
Create protocols for the call types that need scripted questions.
Add a person or organization contact.
Members find the current procedure, preplan or phone number when they need it instead of searching email.
Gather the documents and contacts members need most, and decide who keeps them current.
Categories for organizing contacts.
Members find the current procedure, preplan or phone number when they need it instead of searching email.
Gather the documents and contacts members need most, and decide who keeps them current.
Upload a document.
Members find the current procedure, preplan or phone number when they need it instead of searching email.
Gather the documents and contacts members need most, and decide who keeps them current.
Before you begin: Documents module enabled
Short shared notes for the department.
Members find the current procedure, preplan or phone number when they need it instead of searching email.
Gather the documents and contacts members need most, and decide who keeps them current.
Before you begin: Notes module enabled
Post a department note.
Members find the current procedure, preplan or phone number when they need it instead of searching email.
Gather the documents and contacts members need most, and decide who keeps them current.
Before you begin: Notes module enabled
Create a dispatch protocol.
Members find the current procedure, preplan or phone number when they need it instead of searching email.
Gather the documents and contacts members need most, and decide who keeps them current.
Custom forms used on calls and dispatches.
Members find the current procedure, preplan or phone number when they need it instead of searching email.
Gather the documents and contacts members need most, and decide who keeps them current.
Share selected calls, units and personnel with a linked department.
Review exposed data and link access before distribution.
Gather the documents and contacts members need most, and decide who keeps them current.
Files attached to documents and records.
Keep reference material with its owner, permissions and retention policy.
Gather the documents and contacts members need most, and decide who keeps them current.
Before you begin: Documents module enabled
Ready-made checklists for common checks.
Recorded checks show what was inspected and what was missed.
Start from a template or build a checklist for each apparatus.
Before you begin: Feature access enabled by your system operator
Checklists members complete.
Recorded checks show what was inspected and what was missed.
Create the checklists members complete on paper today.
Before you begin: Feature access enabled by your system operator
Recurring schedules and due checks.
Make recorded equipment and procedure checks visible to their owners.
Schedule each checklist and choose who completes it.
Before you begin: Checklists module enabled
Create a checklist.
Recorded checks show what was inspected and what was missed.
Pick the checks you do on paper today and who completes them.
Before you begin: Feature access enabled by your system operator
Completed, skipped and overdue checks over time.
Find missing recorded checks without treating a report as safety certification.
Pick the checks you do on paper today and who completes them.
Before you begin: Checklists module enabled
Repair and maintenance work orders.
Turn a failed check or reported defect into a tracked repair and a documented return to service.
Create work orders from failed checks or reported defects.
Before you begin: Feature access enabled by your system operator; Maintenance module enabled; Readiness Pro add-on access
Recurring maintenance schedules.
Plan equipment upkeep and track corrective responsibility.
Schedule routine service for each apparatus.
Before you begin: Readiness Pro add-on access; Maintenance module enabled
Repair approvals and safety holds.
Make authority and repair completion requirements explicit.
Decide who approves repairs and returns equipment to service.
Before you begin: Readiness Pro add-on access; Maintenance module enabled
Open a work order.
Turn a failed check or reported defect into a tracked repair and a documented return to service.
Requires the Readiness Pro add-on. Checklists remain available without it.
Before you begin: Feature access enabled by your system operator; Maintenance module enabled; Readiness Pro add-on access
Maintenance history, repair costs and safety holds.
Support accountable return-to-service review through the owning workflow.
Requires the Readiness Pro add-on. Checklists remain available without it.
Before you begin: Readiness Pro add-on access; Maintenance module enabled
The Readiness Pro add-on: work orders, preventive maintenance, repair approvals and safety holds.
Give equipment defects an owner and a recorded repair and return-to-service review.
Checklists do not require this add-on. Maintenance needs its module, permissions and active entitlement. Historical evidence and hold release follow owning-module rules.
Before you begin: Readiness Pro add-on access
Items, stock levels and storage locations.
Know what you have, where it is and what is about to expire.
Add the supplies and equipment you track and where they are stored.
Before you begin: Inventory module enabled
Counts, expiry dates and low-stock alerts.
Identify inventory data and supplies that need owner follow-up.
Set minimum levels and expiry alerts for critical supplies.
Before you begin: Inventory module enabled
What is on hand, running low or expiring.
Know what you have, where it is and what is about to expire.
Decide which supplies and equipment are worth tracking and where they are stored.
Before you begin: Inventory module enabled
Move stock between locations.
Know what you have, where it is and what is about to expire.
Decide which supplies and equipment are worth tracking and where they are stored.
Before you begin: Inventory module enabled
Issue equipment to members and record returns.
Know what you have, where it is and what is about to expire.
Decide which supplies and equipment are worth tracking and where they are stored.
Before you begin: Inventory module enabled
Suppliers, purchase orders and deliveries.
Connect replenishment to recorded stock needs and authorized receipt.
Decide which supplies and equipment are worth tracking and where they are stored.
Before you begin: Inventory module enabled
Activity logs for calls, training and work.
Keep incident and activity records with the calls they came from, ready for review and reporting.
Choose the log types members complete.
Before you begin: Logs module enabled
Incident and activity records.
Keep incident and activity records with the calls they came from, ready for review and reporting.
Turn on Records if it is available to you and review the record settings.
Before you begin: Feature access enabled by your system operator; Logs module enabled
Incident reports linked to calls.
Review source completeness before finalization or external submission.
Decide who completes and who reviews each report.
Before you begin: Feature access enabled by your system operator
The forms and fields records use.
Fit reporting to approved local procedures while preserving built-in definitions.
Start from the built-in forms and add only the fields you need.
Before you begin: Feature access enabled by your system operator; Manage Record Definitions permission
Department reports on calls, personnel and activity.
Keep incident and activity records with the calls they came from, ready for review and reporting.
Run the reports you use for meetings or compliance.
Before you begin: Reports module enabled
Record a run report, training log or work log.
Keep incident and activity records with the calls they came from, ready for review and reporting.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Logs module enabled
Records that are due, awaiting review or ready to submit.
Keep incident and activity records with the calls they came from, ready for review and reporting.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator; Logs module enabled
Numbering, retention, search and visibility rules for records.
Keep incident and activity records with the calls they came from, ready for review and reporting.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator; Logs module enabled
Buildings and sites with their contacts, hazards and preplans.
Keep site knowledge owned and current; recorded hazards do not certify safety.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator
Schedule inspections and track violations and corrections.
Track administrative follow-up against configured inspection procedures.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator
Hydrants and water sources with their inspection and flow history.
Identify records needing verification without claiming current flow or availability.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator
Permits and their approval status.
Assign review responsibility; a software state is not a hazardous-work safety clearance.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator
Restricted case records, such as fire investigations.
Keep case responsibility and access separate from general department visibility.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator
Collect and track evidence attached to a record.
Preserve evidence context and access restrictions without copying it into setup guidance.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator
Legal holds that stop records from being deleted.
Retain affected evidence while a hold remains active.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator; Manage Record Legal Hold permission
Submit incident reports to state or national reporting systems.
Review destination requirements and actual submission outcomes.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator; Submit Records permission
Response, workload and readiness trends from your records.
Use measured source data with its scope and completeness limits.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator
Saved record reports you can run again.
Make repeatable administrative reviews easier.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator; Manage Record Reports permission
Export records to files using templates.
Keep release destinations, protected access and output handling explicit.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator; Manage Record Reports permission
Requests to release records, with redaction and approval.
Assign review ownership and verify the material approved for release.
Know which reports your department completes and who reviews them. Records may need to be enabled for your department.
Before you begin: Feature access enabled by your system operator
Deployment records and Deployment Finance.
Keep deployment records and cost documentation together for review and reimbursement.
Record your next deployment with its personnel and apparatus.
Before you begin: Feature access enabled by your system operator
Start a deployment record.
Keep deployment records and cost documentation together for review and reimbursement.
Useful when your members deploy to incidents outside your jurisdiction.
Before you begin: Feature access enabled by your system operator
Create a deployment from a mutual-aid resource order.
Keep deployment records and cost documentation together for review and reimbursement.
Useful when your members deploy to incidents outside your jurisdiction.
Before you begin: Feature access enabled by your system operator
Customer invoices and payments.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Set up billing settings and rate cards, then create invoices.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Contracts, bids and rate schedules.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Add your service contracts and their rates.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Cal OES MARS reimbursement claims.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Enter your annual rates, then work the MARS action queue after deployments.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Workforce compensation and field cost runs.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Add compensation profiles, then run field costs for deployments.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Create an invoice for a customer.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Rates for units, personnel and fees used on invoices.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Unpaid invoices grouped by how overdue they are.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
The legal name, remit-to address and tax details printed on invoices.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Connect your Stripe account to take invoice payments online.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Priced estimates for customers.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Create a bid for a customer.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Create a service contract for a customer.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Insurance, licences and bonds, with expiry reminders.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Contractor rates for crews, vehicles and equipment.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
MARS claims waiting to be prepared and submitted.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Annual MARS salary and equipment rates.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Match MARS payments to the claims you submitted.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Pay rates and employer costs for staff.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Annual earnings and hours used for pay data reporting.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Running costs for units and equipment.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Work out the full cost of a bid, call or deployment.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access
Prepare California pay data reports. Also requires Advanced Data Protection.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations module enabled; Business Operations add-on access; Advanced Data Protection add-on access; Data protection enrollment completed
Your voluntary answers for California pay data reporting.
Bill for standby and contract services and prepare reimbursement claims from records you already keep.
Requires the Workforce and Business Operations add-on. Online payments also need your own payment-provider account.
Before you begin: Feature access enabled by your system operator; Business Operations add-on access
The Workforce and Business Operations add-on: invoicing, payments, contracts, bids, MARS reimbursement and workforce costing.
Connect administrative commercial work to the department activities it supports.
Certifications and Deployment Finance do not require this add-on. Pay-data reporting additionally needs ADP Enabled; online payments require provider setup. No reimbursement or savings are guaranteed.
Before you begin: Business Operations add-on access
Automations triggered by department events.
Automate repeated administrative steps and connect Resgrid to the other systems you use.
Start with one workflow for a task you repeat, and review its runs.
Custom fields on calls, personnel and other records.
Collect the information the department actually needs with appropriate classification.
Add only the fields you must capture.
API and MCP access for other systems.
Connect approved systems without placing credentials in setup examples.
Create credentials for each integration and limit what they can access.
Create an automation workflow.
Automate repeated administrative steps and connect Resgrid to the other systems you use.
Have the destination systems and credentials ready, and decide who owns each automation.
The history of workflow runs, including failures.
Automate repeated administrative steps and connect Resgrid to the other systems you use.
Have the destination systems and credentials ready, and decide who owns each automation.
Plan moving your data from another system into Resgrid.
Avoid duplicate resources and verify resulting configuration in Setup Report.
Have the destination systems and credentials ready, and decide who owns each automation.
Push-to-Talk voice channels.
Coordinate field teams through app-based voice channels.
Create channels and add the members who use them.
Before you begin: Push-to-Talk add-on access
The Push-to-Talk add-on: voice channels in the Resgrid apps.
Coordinate field teams through configured voice channels.
Review seats, supported clients and channel setup. PTT does not provide phone dispatch alerts or certify radio replacement.
Before you begin: Push-to-Talk add-on access
Protection enrollment, key recovery and access controls.
Protects sensitive incident and personnel content, with controlled disclosure and key recovery.
Review the enrollment checklist and plan key recovery before enrolling.
Before you begin: Advanced Data Protection add-on access
Send protected data to approved outside systems through reviewed workflows.
Keep protected-data egress scoped, reviewed and auditable.
Requires the Advanced Data Protection add-on. Enrollment is a separate step: plan two-factor sign-in and key recovery first, and review the effects on search, exports and integrations.
Before you begin: Advanced Data Protection add-on access; Data protection enrollment completed
The Advanced Data Protection add-on: extra encryption and controlled access for sensitive data.
Control protected content disclosure and recovery through the department protection lifecycle.
Buying does not enroll the department. Review MFA, recovery, migration and integration behavior; this is not a compliance certification.
Before you begin: Advanced Data Protection add-on access
Your plan, its personnel and unit limits, and your add-ons.
Choose capacity for actual department needs without inferring prices or terms.
Check the remaining room before adding many members or units.
AI assistance beyond the free Admin Assist allowance.
Help explain approved evidence and prepare drafts for human review when released.
Nothing to set up yet; your free Admin Assist allowance works without it.
Before you begin: Enhanced AI add-on access
Availability: planned. Check your department’s version and enabled modules.
Passkeys add a device-backed sign-in factor and need deliberate naming, removal, and recovery handling.
Passkeys add a device-backed sign-in factor and need deliberate naming, removal, and recovery handling.
Enroll from account security on a compatible demo device. Name the credential and review the remaining recovery factors.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Account linking associates a member with a configured external assistant platform.
Account linking associates a member with a configured external assistant platform.
Confirm a platform is configured, generate a short-lived linking code, and complete linking in the intended platform.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Connect provides a department profile, posts, and communication surfaces.
Connect provides a department profile, posts, and communication surfaces.
Review the intended public profile content, then prepare a fictional profile and sample post through their owning screens.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Navigation search helps members find the work they are authorized to access.
Navigation search helps members find the work they are authorized to access.
Search for a known department feature using a member account and an administrator account.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Resource orders describe requested resources and the fills departments offer or accept.
Resource orders describe requested resources and the fills departments offer or accept.
Review ordering settings and participating departments. Create a fictional request, offer a fill, and review acceptance.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
An external order records the department fills and their mobilization, release, and actual return home.
An external order records the department fills and their mobilization, release, and actual return home.
Enter an approved sample external order, link its deployment, record the fill transitions, and complete closeout.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Read-only deployment reports bring time entries, supporting artifacts, and export outputs together.
Read-only deployment reports bring time entries, supporting artifacts, and export outputs together.
Open a recorded demo deployment and review its time report, summary, and available exports.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Post-finalization review uses rubrics, sampling, scores, and trends to identify reporting follow-up.
Post-finalization review uses rubrics, sampling, scores, and trends to identify reporting follow-up.
Confirm rollout and reviewer access, configure an approved rubric, sample finalized records, and score a demo review.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Records health and prevention attachment screens make retained record support and issues visible to authorized users.
Records health and prevention attachment screens make retained record support and issues visible to authorized users.
Review the records health view and attach a synthetic support file to an appropriate prevention record.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Incident analysis is a separately validated and submitted artifact linked to an incident report.
Incident analysis is a separately validated and submitted artifact linked to an incident report.
Start analysis from a demo incident, edit and validate it, then review finalization and submission readiness.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Community risk reduction records education and prevention activity with attendee counts.
Community risk reduction records education and prevention activity with attendee counts.
Confirm the community-risk feature and access, record a fictional activity, and review its summary and analytics scope.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Revision and difference views help reviewers understand how a record changed.
Revision and difference views help reviewers understand how a record changed.
Open two revisions of a synthetic record and review their differences and any permitted export.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Submission details and reconciliation keep a recorded report distinct from its external filing outcome.
Submission details and reconciliation keep a recorded report distinct from its external filing outcome.
Review a test submission status and reconcile a known destination response through the owning workflow.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Record inventory workflows connect consumption and evidence to the incident or activity record.
Record inventory workflows connect consumption and evidence to the incident or activity record.
Link synthetic inventory use to a record, refresh its evidence, and review supported reversal handling.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Deployment connector screens manage connector configuration, enablement, tokens, and runs.
Deployment connector screens manage connector configuration, enablement, tokens, and runs.
Review connector terms and ownership, configure a demo destination, and inspect a controlled run.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Work-order operations connect parts, vendor charges, approval requests, and spending policy to a repair.
Work-order operations connect parts, vendor charges, approval requests, and spending policy to a repair.
Review policy, reserve a sample part, record its movement and a vendor charge, then request the required approval.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Bulk maintenance tools preview imported rows or assignment changes before applying them.
Bulk maintenance tools preview imported rows or assignment changes before applying them.
Use the import template or select demo rows, preview the proposed changes, and review the row outcomes.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
The checkout contains gated AI dispatch settings for enrichment fields, confidence, sender scope, token limits, and activity.
The checkout contains gated AI dispatch settings for enrichment fields, confidence, sender scope, token limits, and activity.
Confirm host enablement and department rollout before reviewing the settings. Saving settings alone does not start enrichment.
Availability: source-present; deployment unverified. Check your department’s version and enabled modules.
Make informed choices
Review a setting’s purpose and its effects before changing your department configuration.
Disabled Auto Available. Disables automatic availability behavior. Review staffing/status reset interactions before changing it.
Personnel Sort Order. Sort order for personnel lists; does not change availability, access or dispatch priority.
Personnel List Status Sort Order. Custom ordering of personnel statuses in lists. Review all configured statuses before replacing the order.
Staffing Suppress Staffing Levels. Staffing levels suppressed in supported notifications. Suppression can change who hears an alert and is not evidence of delivery.
Personnel List Status Order Setting / Orders. Ordered status weights for supported personnel lists. This does not set availability or dispatch priority.
Personnel List Status Order / Weight. Relative list order for this status. Confirm all configured statuses remain represented.
Personnel List Status Order / Status ID. Existing personnel-status identifier whose list position is being configured.
Department Suppress Staffing Info / Enable Suppress Staffing. Enables the configured staffing-level suppression in supported notification consumers; review reachability before changing it.
Department Suppress Staffing Info / Staffing Levels To Suppress. Existing staffing levels to suppress. A suppressed level is not proof that another channel reaches the member.
Department / Address ID. Department address reference. Review the owning address and mapping consumers; it is separate from station and site addresses.
Test Enabled. Department testing behavior. Do not treat enabling a test setting as proof of production readiness.
Update Timestamp. Internal configuration timestamp. Read-only metadata, not an administrator-editable preference.
Module Settings. Controls module navigation and supported feature gates. Hiding a module does not delete its records or prove independent dispatch settings are disabled.
Require2 FAFor Admins. Administrator MFA requirement mode. Verify actual factors and recovery for each administrator before enforcement changes.
Force Chatbot Security Pin. Require the member security PIN for sensitive supported chatbot and SMS actions, including members who have not opted in.
Require Password Reset Via Email. Use single-use recovery links for administrator-initiated member password resets, instead of selecting a replacement password.
Department Operating Profile. Declared organization, workforce, dispatch, seasonal, language and policy context. Recommendations never infer licenses or clinical scope from this profile.
Operating sectors. Choose all sectors served by the department. A pack suggests administrative reviews; it does not establish qualification or clinical scope.
Workforce mix. Describe the workforce so setup guidance can reflect career, volunteer, contract or combined operations.
Declared member count. Optional planning estimate; actual membership and subscription counts come from their owning sources.
Authoritative system references. Short declared source-system labels. Saving this list does not verify a connection, an import or the freshness of external data.
Dispatch model. Record whether dispatch is central, self-directed, external or a combination. Verify each routing path through its owning settings.
Operating hours. Describe continuous, scheduled, on-call or seasonal operation. This is context and does not create shifts or guarantee coverage.
Sites and groups. Reference existing numeric group IDs in this department. This does not grant group access or change dispatch scope.
Mutual aid participation. Declare whether mutual aid is part of operations. Agreements, access and response eligibility require separate review.
Working languages. Languages used by the team. This preference does not prove interpreter availability or translate operational records.
Accessibility preferences. Record screen-reader, caption, large-text or plain-language needs for setup planning. Verify client behavior with the people who use it.
Staffing policy documents. Reference existing department document IDs for approved staffing policies. The save checks existence and expiry, not policy approval or adequacy.
Qualification policy documents. Reference existing department document IDs for approved qualification policies. Do not infer a license, scope of practice or deployment qualification from a role label.
Continuity procedure documents. Reference existing department document IDs for approved continuity procedures. Test fallback communications and ownership through the approved procedure.
Season start. Start of a declared seasonal period, in MM-DD format. Provide both start and end; this does not enable or disable resources on those dates.
Season end. End of a declared seasonal period, in MM-DD format. A period can cross a calendar year; verify actual rosters separately.
Profile review time. Server-recorded time of the most recent validated profile save; it does not certify operational readiness.
Profile revision. Server revision used to reject concurrent overwrites. Reload when another administrator has saved a newer profile.
Expected email polling interval (minutes). Optional maximum time between recorded mailbox polls, from 1 to 10080 minutes. Blank means no declared polling expectation. This checks configured email connectors, not how often calls arrive; it does not measure SMS, CAD push or API health. Review the host polling schedule before setting it.
Create calls. Allows starting a call. The department-level action uses each member’s actual administrator state and personnel roles; later dispatch validation remains authoritative.
Create notes. Allows creating a department note. The action does not grant access to protected note contents or another department.
View personal information. Controls the personal-information permission gate. Protected fields still require their own current authorization and data protection grant.
View personnel. Controls visibility of personnel targets. A group lock can narrow target scope; administrators of a target group or its ancestors use the owning visibility policy.
View units. Controls visibility of unit targets and their assigned stations. Ungrouped viewers and unassigned units do not share a group.
View personnel locations. Controls the location visibility gate for each viewer and person. The preview counts access pairs, not current map markers, tracking consent or GPS availability.
View unit locations. Controls the location visibility gate for each viewer and unit. A group lock refers to the unit’s station and the owning group hierarchy, not any station a viewer can otherwise see.
Add Personnel. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Remove Personnel. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Create Training. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Create Document. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Create Calendar Entry. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Create Log. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Create Shift. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Adjust Inventory. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Create Message. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Delete Call. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Close Call. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Add Call Data. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Contact Edit. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Contact View. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Contact Delete. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Create Workflow. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Workflow Credentials. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Workflow Runs. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View custom field Fields. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Routes. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Delete Log. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Use Calendar Sync. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Dispatch App Login. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Command App Login. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Department Data Protection. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Protected Call Data. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Edit Protected Call Data. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Protected Personnel Data. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Protected Contact Data. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Protected Operational Data. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Export Protected Data. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Configure Protected Data Egress. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Break Glass Protected Data. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Create Record. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Delete Record. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Review Records. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Approve Records. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Finalize Records. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Amend Records. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Submit Records. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Export Records. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Share Records Externally. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Restricted Records. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Legacy Records. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Group Records. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Record Definitions. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Publish Record Definitions. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Record Reports. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Record Disclosures. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Record Legal Hold. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Reassign Record Drafts. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Records Prevention Admin. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Checklists. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Checklist Results. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Work Orders. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View All Work Orders. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Transfer Inventory. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Issue Inventory. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Controlled Substances. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Invoicing. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Invoicing. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Certifications. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Certifications. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Certification Setup. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Bids. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Contracts. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Deployments. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Approve Time Reports. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Mutual Aid Reimbursement. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Internal Costs. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Workforce Compensation. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
View Workforce Compensation. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Manage Pay Data Reporting. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Export Pay Data Reporting. Review this permission on the Security screen. Its default when no policy is saved, group scope, dependent permissions and behavior across web, API and mobile are awaiting a complete consumer review. No live impact preview is available for this permission yet.
Department / Name. Department display name. Review member-facing labels and documents that snapshot the name; changing it does not rename historical artifacts.
Department / Department Type. Legacy organization-type label. The operating profile provides multiple sectors; neither establishes clinical scope or response qualifications.
Department / Time Zone. Department time zone used by scheduling and local-date reports. Review overnight shifts and daylight-saving transitions before changing it.
Department / Use24 Hour Time. Preferred time display. This does not change stored timestamps or the department time zone.
Department / Managing User ID. Managing-member identity. Subscription and high-risk account operations may require this member; change ownership through its explicit owning workflow.
Department / Code. Department code used by supported identification and access flows. Review those consumers before changing it.
Department / API Key. Department API credential. Never place it in setup notes or model input; manage and rotate it through the authorized workflow.
Department / Public API Key. Credential used by supported public API consumers. Public in the field name does not make credential disclosure safe.
Department / Shared Secret. Department integration secret. Rotation can affect integrations and needs coordinated verification.
Department / Link Code. Department linking code. Review who can use a link and rotate it using the owning workflow.
Department / Show Welcome. Legacy welcome flag. Restored setup dismissal is per administrator and does not use this flag as evidence of setup completion.
Department Security Policy / Require MFA. Department-wide MFA policy, distinct from the administrator-only setting. Review enrollment, supported factors and recovery before enforcement.
Department Security Policy / Require SSO. Requires the supported SSO policy gate. Verify the active identity provider and local recovery arrangements before removing a sign-in path.
Department Security Policy / Session Timeout Minutes. Idle timeout in minutes; zero defers to host behavior. Verify policy-managed sessions and each supported client rather than assuming immediate global logout.
Department Security Policy / Max Concurrent Sessions. Maximum policy-managed concurrent sessions per user; zero means unlimited for this setting. Existing sessions and enforcement rollout must be checked separately.
Department Security Policy / Allowed IP Ranges. Allowed login network ranges. Empty adds no range restriction. Review legitimate responder networks and recovery access before narrowing it.
Department Security Policy / Password Expiration Days. Password age in days; zero disables this policy's age limit. Verify local-password and SSO behavior separately.
Department Security Policy / Min Password Length. Minimum length offered by the policy editor. Actual password validators and supported credential-change paths remain authoritative.
Department Security Policy / Require Password Complexity. Stored complexity preference. Consumer and editor coverage must be verified before relying on this field; it is not proof that an existing password meets a rule.
Department Security Policy / Data Classification Level. Department classification label. Selecting it does not enroll ADP, establish compliance or automatically classify every record correctly.
Department Security Policy / Allow Passkeys For Login MFA. Accepts a passkey registered in the requesting app as MFA for sign-in, department entry and step-up. Authenticator codes are always accepted. Changing it advances the MFA policy version; sessions whose only second factor is now disallowed verify again. Managing member only.
Department Security Policy / Allow Passkeys For ADP. Accepts a passkey for protected-data access, ADP management and protected-workflow approvals. Authenticator codes are always accepted. Changing it ends current protected-data access, so members verify again. Managing member only.
Department Security Policy / Allow Federated MFA For Login MFA. Accepts the identity provider's MFA for sign-in and step-up. Requires a tested MFA mapping on the SSO configuration; without one the provider's claims never count. Managing member only.
Department Security Policy / Allow Federated MFA For ADP. Accepts the identity provider's MFA for protected data. Requires a tested MFA mapping; changing it ends current protected-data access. Managing member only.
Department Security Policy / Allow Responder Approval. Accepts approval with the member's Responder app passkey wherever the matching passkey setting is on; never for security changes or account sign-in methods. Changing it also ends current protected-data access. Managing member only.
Department Security Policy / Accept Recent Login MFA For ADP. Lets MFA completed at sign-in in the same session open protected data within the step-up window, for methods the protected-data settings allow. Changing it ends current protected-data access. Managing member only.
Department Security Policy / Accept Recent Unlock MFA For ADP. Lets the operator's fresh unlock verification on a shared device open protected data. Changing it ends current protected-data access. Managing member only.
Department Security Policy / Shared Idle Lock Minutes. Minutes without operator activity before a shared vehicle tablet or workstation session locks, from 1 to 15. Background updates and incoming alerts are not activity. A stricter value reaches running sessions at their next request. Managing member only.
Department Security Policy / Shared Shift Hours. Hours after sign-in when a shared session ends whatever the activity, from 1 to 24. A shorter value ends running sessions sooner; a longer one never extends them. Managing member only.
Department Security Policy / Shared Mode Required Apps. Unit, IC and Dispatch sessions this department always runs as shared sessions, whatever the installation is set to; sign-ins that do not name their app count too. Needs app versions that support shared mode. Managing member only.
Department SSO Config / SSO Provider Type. Selects the identity protocol and provider configuration. OIDC and SAML have different metadata, certificates and callback requirements.
Department SSO Config / Is Enabled. Makes this provider configuration available to the supported SSO flow. A saved enabled flag is not a successful sign-in test.
Department SSO Config / Client ID. Client registration identifier from the identity provider. Keep tenant and audience registration consistent with the owning SSO flow.
Department SSO Config / Encrypted Client Secret. Encrypted provider client secret. The secret is entered and rotated on the authorized provider editor; Admin Assist only describes its purpose.
Department SSO Config / Authority. OIDC issuer or authority. Verify the intended tenant, discovery metadata and callback registration before enabling it.
Department SSO Config / Metadata URL. SAML provider metadata location. Review the trusted provider and its current signing material through the SSO editor.
Department SSO Config / Entity ID. SAML service-provider identifier registered at the identity provider. It must agree with the configured integration.
Department SSO Config / Assertion Consumer Service URL. Stored SAML callback configuration. Use the endpoint supplied by the owning SSO setup and verify the provider registration.
Department SSO Config / IdP SSO URL. SAML provider sign-in address that sign-in started from Resgrid sends its request to. Verify it against the provider metadata before relying on it.
Department SSO Config / Encrypted IdP Certificate. Encrypted provider verification certificate material. Review expiry and rotation through SSO; this description is not certificate validation.
Department SSO Config / Encrypted Signing Certificate. Encrypted signing certificate and private-key material. Do not copy it into notes, logs or assistant messages.
Department SSO Config / Attribute Mapping JSON. Maps provider attributes to supported member fields. Validate identity matching and missing attributes with an approved test account.
Department SSO Config / Federated MFA Mapping JSON. Which provider sign-in results count as MFA for provider step-up. A changed mapping, issuer or client needs a new successful test before provider MFA is accepted again.
Department SSO Config / Allow Local Login. Allows a local-password path alongside this provider where policy permits. Review the department-wide SSO requirement and recovery plan together.
Department SSO Config / Auto Provision Users. Allows the supported sign-in flow to create members. Review identity matching, capacity and default assignments before enabling it.
Department SSO Config / Default Rank ID. Department rank assigned by supported automatic provisioning. It does not grant permissions or prove qualifications.
Department SSO Config / SCIM Enabled. Enables supported SCIM provisioning for this configuration. Review identity lifecycle, deactivation and token access separately from interactive sign-in.
Department SSO Config / Encrypted SCIM Bearer Token. Encrypted credential for inbound SCIM requests. Rotate through the explicit token workflow and update the provider before retiring an old credential.
Units Sort Order. Sort order for unit lists; does not change unit eligibility or dispatch recommendation ranking.
Big Board Map Zoom Level. Initial Big Board map zoom. An unset override lets the consuming board select its default.
Big Board Page Refresh. Big Board refresh interval. Review load and the age of displayed information before changing it.
Big Board Map Center Address. Address used to center the Big Board. Address details remain on their owning screen.
Big Board Hide Unavailable. Hide unavailable resources on the Big Board; this affects visibility, not their dispatch eligibility.
Big Board Map Center Gps Coordinates. Explicit board-center coordinates take precedence over address geocoding. Partial coordinates do not overwrite the saved center.
Rss Feed Key For Active Calls. Credential for the active-call feed. Treat the feed and its key as sensitive; rotate through its owning screen.
Text To Call Number. Provisioned inbound text number. Provisioning has external effects and must use the normal text settings flow.
Text To Call Import Format. Parser used for inbound text call creation. Verify the sender format with a controlled example on the owning screen.
Text To Call Source Numbers. Allowed inbound source numbers for text calls and commands. Empty sources prevent accepted intake; never display raw numbers in Admin Assist.
Enable Text To Call. Configured text-call preference. Enforcement differs by provider and chatbot path; the stored value alone does not prove intake is stopped or accepted. Review sender classification and perform an explicit controlled verification on the owning screen.
Internal Dispatch Email. Assigned internal dispatch email address. Presence can be shown; the address stays on the authorized import screen.
Calls Sort Order. Sort order for displayed calls; does not reorder provider delivery or change call priority.
Dispatch Shift Instead Of Group. Expand dispatched groups using the resolved on-duty roster. An empty shift result falls back to group members; preview both cases.
Auto Set Status For Shift Dispatch Personnel. Apply the configured status to shift-dispatched personnel. This only takes effect with shift dispatch enabled.
Shift Call Dispatch Personnel Status To Set. Personnel status applied when shift dispatch occurs. Minus one leaves status unchanged; use an existing approved status.
Shift Call Release Personnel Status To Set. Personnel status applied on call release for the shift-dispatch path. Minus one leaves status unchanged.
Unit Dispatch Also Dispatch To Assigned Personnel. Expand unit dispatch to its assigned crew. Review duplicate routes, current assignments and recipient permissions.
Unit Dispatch Also Dispatch To Group. Expand unit dispatch to the station group. This can substantially increase the recipient audience.
Check In Timers Auto Enable For New Calls. Automatically start configured check-in timers for new calls. Review timer targets and escalation before enabling it.
Unit Call Dispatch Status To Set. Unit status applied during call dispatch. Minus one or an invalid built-in unit status leaves the status unchanged.
Unit Call Release Status To Set. Unit status applied at call release. Review unit-type overrides before assuming one department-wide effect.
Unit Call Status Overrides By Unit Type. Per-unit-type call status overrides. Existing type-specific values take precedence over department defaults.
Dispatch Recommendation Mode. Dispatch recommendation selection mode. Review run cards, eligible resources and human dispatch responsibility.
Dispatch Recommendation Auto Dispatch. Allow the recommendation path to dispatch automatically where enabled. Preview recipients and verify local procedures first.
Dispatch Recommendation Config. Location, ETA, rest, crew and move-up settings used by recommendation consumers. External ETA calls occur only in the owning operational flow.
New Call Field Policy. Controls optional new-call fields across supported clients. Hidden fields cannot be required; core dispatch fields remain mandatory.
Group Dispatch Scope Config. Group-subtree dispatch visibility with explicit role exceptions. Preview each actor and target scope before changing it.
Unit Type Call Status Override Setting / Overrides. Per-unit-type dispatch and release status overrides. The owning consumer resolves these before department defaults.
Unit Type Call Status Override / Unit Type ID. Existing unit type receiving this override. A unit type name is not a qualification or staffing clearance.
Unit Type Call Status Override / Dispatch Status. Status applied to this unit type on dispatch; minus one leaves it unchanged.
Unit Type Call Status Override / Release Status. Status applied to this unit type on release; minus one leaves it unchanged.
New Call Field Policy / Rules. Per-field visibility and requiredness for optional call-creation fields. Unconfigured fields remain visible and optional.
New Call Field Rule / Key. One supported built-in call-field key. Name, nature, priority and type cannot be removed through this policy.
New Call Field Rule / Visible. Whether the optional call field is shown on supported creation surfaces. Hidden fields cannot be required.
New Call Field Rule / Required. Whether a visible optional field must be supplied. Review imports and each supported client before making a field mandatory.
Group Dispatch Scope Config / Enabled. Limit supported dispatch views to the member's group subtree. Department administrators and configured department-wide roles keep department-wide access.
Group Dispatch Scope Config / Department Wide Role IDs. Existing roles allowed department-wide dispatch views while group scoping is enabled. This changes view scope, not licensing or operational qualification.
Dispatch Recommendation Config / Max Location Age Seconds. Exclude older unit positions from closest-unit candidates; zero removes the age limit. IncludeStaleLocations changes this behavior.
Dispatch Recommendation Config / Max Radius Meters. Maximum candidate distance in meters; zero removes the radius cap. This is not a response-time or route-safety guarantee.
Dispatch Recommendation Config / Include Stale Locations. Permit positions beyond the configured age limit in closest-unit selection, marked stale. Review the risk of outdated positions.
Dispatch Recommendation Config / Personnel Max Location Age Seconds. Maximum age of personnel positions for closest-unit candidate selection; zero removes the age limit.
Dispatch Recommendation Config / Use Routed ETA. Re-rank shortlisted candidates using provider travel estimates. The operational path can make external provider calls; Admin Assist does not.
Dispatch Recommendation Config / ETA Shortlist Size. Number of straight-line candidates per requirement sent for routed ETA when enabled. The owning validator caps provider work.
Dispatch Recommendation Config / Rest Period Minutes. Deprioritize recently dispatched resources for this duration; zero disables rotation. This does not infer fatigue or medical fitness.
Dispatch Recommendation Config / Unit Minimum Staffing Level. Minimum configured unit staffing level for recommendation eligibility; zero disables the gate. Units without defined seats pass, and run cards may override it.
Dispatch Recommendation Config / Move Up Recommendations Enabled. Run the station coverage move-up pass after selection. Recommendations remain subject to approved local dispatch procedures.
Department Call Email / Hostname. Mailbox host for email intake. Review the approved provider and network reachability without exposing credentials in setup guidance.
Department Call Email / Port. Mailbox connection port. It must match the selected provider and TLS mode.
Department Call Email / Use SSL. Mailbox transport encryption option. Verify actual provider compatibility and successful polling; a stored flag alone does not prove transport protection.
Department Call Email / Username. Mailbox account identifier used for intake. It remains on the authorized configuration screen.
Department Call Email / Password. Mailbox credential. Do not copy it into Admin Assist; rotate it through the mailbox and owning editor together.
Department Call Email / Format Type. Selects the inbound email parser. Verify representative permitted source messages without sending an operational page unintentionally.
Department Call Email / Last Check. Last recorded polling timestamp. Missing or future timestamps are unknown; quiet call volume is not proof of a poll failure.
Department Call Email / Is Failure. Latest recorded mailbox failure flag. Verify a new poll before treating it as a continuing outage or a resolved problem.
Department Call Email / Error Message. Provider/import error details on the authorized screen. Admin Assist uses a normalized failure indication and does not copy provider bodies.
Personnel On Unit Set Unit Status. Allow personnel status updates to influence their assigned unit status. Review automation and crew assignment together.
Enable Text Command. Configured text-command preference. Dispatch-source patterns and verified member command identity are different checks. Provider and chatbot paths do not enforce this switch uniformly; review the active consumer before changing it.
Tts Language. Text-to-speech language for supported voice notifications. Confirm supported voices and pronunciation with a human-run test.
Enable Modern Notifications. Use supported modern notification behavior. Verify each consumer and channel; provider acceptance is not delivery.
Messaging availability. Controls availability of messages and announcements. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Messaging menu name. Optional display name for messages and announcements in consumers that support the override. It changes the label, not permissions or functionality. This release has no separate name-override control in Module Settings.
Department Notification / Event Type. Event that can trigger this notification rule. Match the event to a real administrative responsibility and expected frequency.
Department Notification / Users To Notify. Explicit member recipients. Membership and channel eligibility are evaluated separately at send time.
Department Notification / Roles To Notify. Personnel-role recipients. Role membership can change; a role label is not a qualification or delivery guarantee.
Department Notification / Groups To Notify. Department-group recipients. Review group membership and lock-to-group behavior together.
Department Notification / Lock To Group. Restricts applicable event processing to group scope. Review the selected event's actual source group and recipient resolver.
Department Notification / Selected Groups Admins Only. Limits selected-group recipients to their administrators in supported event paths. It does not designate department administrators automatically.
Department Notification / Department Admins. Includes department administrators in supported notification processing. Review overlap and channel eligibility before estimating volume.
Department Notification / Everyone. Selects the department-wide recipient option. Review actual active membership, suppression and deduplication before use.
Department Notification / Disabled. Stored disabled marker. The inspected legacy notification processor does not consult this flag, so it must not be treated as a verified stop switch. Review the active consumer; queued and delivered notifications cannot be recalled.
Department Notification / Before Data. Previous-state filter for applicable events. Review valid status IDs and the event-specific interpretation of an empty or wildcard value.
Department Notification / Current Data. Current-state filter for applicable events. Compare it with the previous-state filter to avoid unintended volume.
Department Notification / Upper Limit. Upper threshold for event-specific alerts. Units and comparisons depend on the selected event.
Department Notification / Lower Limit. Lower threshold for event-specific alerts. Use approved local thresholds and verify the actual event interpretation.
Department Notification / Data. Event-specific configuration payload. The owning editor validates its meaning; Admin Assist does not execute arbitrary stored expressions.
Chatbot Department Config / Is Enabled. Department chatbot availability. Platform feature rollout, account linking and action permissions are separate gates.
Chatbot Department Config / Allowed Platforms. Allowed chatbot platform codes; the stored asterisk represents the platform default. Review each connected provider and its account-linking requirements.
Chatbot Department Config / Max Sessions Per User. Maximum chatbot sessions per member in supported consumers. This is separate from authenticated web/mobile session limits.
Chatbot Department Config / Session TTL Minutes. Chatbot session lifetime in minutes. Expiry does not revoke an unrelated Resgrid sign-in session.
Chatbot Department Config / Allow Dispatch Via Chatbot. Permits supported chatbot dispatch actions subject to their own authorization and confirmation. Enabling it may allow real calls and pages.
Chatbot Department Config / Require Confirmation For Status Change. Requests confirmation for supported status changes. Review each platform consumer before assuming all commands are covered.
Chatbot Department Config / LLM API Endpoint. Optional existing chatbot model endpoint. Phase 0 Admin Assist does not call it and does not use chatbot configuration as an AI entitlement.
Chatbot Department Config / LLM API Key. Credential for the chatbot model provider. Never copy it into setup metadata or public reference content.
Chatbot Department Config / LLM Model Name. Model identifier used by the existing chatbot integration. This is separate from the later Admin Assist open-source inference deployment.
Chatbot Department Config / Messages Per User Per Minute. Optional per-member chatbot rate bound. Review provider limits and burst behavior; this is not a delivery guarantee.
Chatbot Department Config / Messages Per Department Per Minute. Optional department chatbot rate bound. Consider shared demand and provider quotas before changing it.
Chatbot Department Config / Require Linking Confirmation. Requires confirmation in the supported account-linking flow. Linking must not bypass verified identity or departmental authorization.
Chatbot Department Config / Proactive Notifications Enabled. Allows supported proactive chatbot notifications. Recipient permissions, channel configuration and sending workflows remain authoritative.
Mapping Personnel Location TTL. Maximum personnel location age in minutes. Zero keeps stale positions visible without an age limit; assess actual ping ages.
Mapping Unit Location TTL. Maximum unit location age in minutes. Zero retains stale unit locations indefinitely in supported map consumers.
Mapping Personnel Allow Status With No Location To Overwrite. Allow a personnel status without a location to replace the previous location-bearing state. This can remove a marker.
Mapping Unit Allow Status With No Location To Overwrite. Allow a unit status without a location to overwrite earlier location data. Check hardware and app updates together.
Weather Alerts Enabled. Enable supported weather-alert processing. Configure zones and communication behavior before relying on it.
Weather Alert Minimum Severity. Minimum severity eligible for the weather-alert view. Severity values come from the weather service, not local incident triage.
Weather Alert Auto Message Severity. Minimum weather severity eligible for automatic messages. Review recipients, schedule and duplicate suppression.
Weather Alert Call Integration. Include supported weather context in call integration. It does not certify weather or route safety.
Weather Alert Cache Minutes. Weather cache duration; longer caching changes freshness and provider load.
Weather Alert Auto Message Schedule. Schedule for automatic weather messaging. Review the department time zone, overnight periods and daylight-saving changes.
Weather Alert Excluded Events. Weather event types excluded from configured processing. Review exclusions against approved local procedures.
Mapping Use Mapbox Override. Use the department map provider override. Turning it off on the owning screen removes the stored style and token.
Mapping Mapbox Style Url. Custom map style reference. Verify the provider style and credential together; disabling the override deletes this value.
Mapping Mapbox Access Token. Map-provider access token. Only presence is reported. Disabling the override deletes it and requires re-entry to restore.
Hardware Tracking Stale After Seconds. Age at which a hardware location becomes stale, clamped to at least one second. Review device reporting intervals.
Hardware Tracking Mobile Fallback Enabled. Use supported mobile location fallback when hardware data is stale. Verify each device/source rather than assuming continuous tracking.
Hardware Tracking Location Retention Days. Tracking retention bounded by host configuration and applicable holds. Shortening retention can make data eligible for deletion.
Unit Status Thresholds. Visual warning thresholds for time in a unit status. A highlight does not change the unit status or certify availability.
Mapping availability. Controls availability of maps and location views. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Mapping menu name. Optional display name for maps and location views in consumers that support the override. It changes the label, not permissions or functionality. This release has no separate name-override control in Module Settings.
Unit Status Thresholds / Thresholds. Board highlighting thresholds grouped by base status meaning. An empty list disables highlighting.
Unit Status Threshold / Base Type. Base status meaning for a threshold, independent of custom status names and colors.
Unit Status Threshold / Warn Seconds. Seconds in this status before a warning highlight; zero disables it. An alert at or before this threshold makes the row alert-only.
Unit Status Threshold / Alert Seconds. Seconds in this status before a higher-priority highlight; zero disables it. Highlighting does not send a page or change status.
Weather Alert Zone / Name. Administrator-facing label for this weather zone. The name does not define its geographic coverage.
Weather Alert Zone / Zone Code. Provider weather-zone identifier. Verify the intended jurisdiction and source coverage.
Weather Alert Zone / Center Geo Location. Center point used by supported radius-based weather coverage. Coordinate values stay on their owning map/editor.
Weather Alert Zone / Radius Miles. Radius in miles for supported geographic matching. Review actual coverage and provider behavior; larger is not automatically safer.
Weather Alert Zone / Is Active. Whether the zone participates in supported weather processing. Department weather settings and worker operation are additional requirements.
Weather Alert Zone / Is Primary. Marks the primary zone for consumers that select a default. Review other active zones rather than assuming they are disabled.
Allow Signups For Multiple Shift Groups. Allow a member to sign up for multiple shift groups. Review overlaps and local coverage rules separately.
Shifts availability. Controls availability of shift scheduling. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Shifts menu name. Optional display name for shift scheduling in consumers that support the override. It changes the label, not permissions or functionality. This release has no separate name-override control in Module Settings.
Calendar availability. Controls availability of calendar events. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Calendar menu name. Optional display name for calendar events in consumers that support the override. It changes the label, not permissions or functionality. This release has no separate name-override control in Module Settings.
Training availability. Controls availability of training. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Training menu name. Optional display name for training in consumers that support the override. It changes the label, not permissions or functionality. This release has no separate name-override control in Module Settings.
Documents availability. Controls availability of shared documents. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Documents menu name. Optional display name for shared documents in consumers that support the override. It changes the label, not permissions or functionality. This release has no separate name-override control in Module Settings.
Notes availability. Controls availability of notes. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Notes menu name. Optional display name for notes in consumers that support the override. It changes the label, not permissions or functionality. This release has no separate name-override control in Module Settings.
Checklists availability. Controls availability of checklists. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Maintenance availability. Controls availability of maintenance and work orders. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Maintenance menu name. Optional display name for maintenance and work orders in consumers that support the override. It changes the label, not permissions or functionality. This release has no separate name-override control in Module Settings.
Inventory availability. Controls availability of inventory. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Inventory menu name. Optional display name for inventory in consumers that support the override. It changes the label, not permissions or functionality. This release has no separate name-override control in Module Settings.
Records Default Lifecycle Preset. Default lifecycle for new department-owned definitions. Locked definitions retain their own lifecycle.
Records Review Due Hours. Default administrative review deadline; a definition-level override takes precedence. This is not a statutory deadline inference.
Records Numbering Config. Number assignment, year reset and sequence formatting for definitions that do not override the department configuration.
Records Search Config. Allowed record search scope and protected-data behavior. Search access remains bounded by current source permissions.
Records Retention Policy. Default and definition-specific retention, including prior-policy history. Holds and restricted-class rules can prevent purge eligibility.
Records Group Visibility Mode. Whether record visibility is department-wide or group scoped. Group scope narrows existing permission and never grants access.
Records Group Scope Config. Reserved identifier with no editable behavior in this release. Do not present it as a shipped setting.
Records Disclosure Config. Disclosure review clock, redaction profile and release approver. Review local obligations through the authorized disclosure workflow.
Logs availability. Controls availability of legacy logs. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Logs menu name. Optional display name for legacy logs in consumers that support the override. It changes the label, not permissions or functionality. This release has no separate name-override control in Module Settings.
Reports availability. Controls availability of reports. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Reports menu name. Optional display name for reports in consumers that support the override. It changes the label, not permissions or functionality. This release has no separate name-override control in Module Settings.
Records Numbering Config / Number Assignment. Choose when numbers are assigned for definitions using department defaults. Review existing references before changing numbering behavior.
Records Numbering Config / Reset Yearly. Restart record sequences each calendar year in the department time zone.
Records Numbering Config / Sequence Width. Zero-padded sequence width for definitions using department defaults. The Records editor validates the supported width.
Records Numbering Config / Include Year. Include the year between the record prefix and sequence number.
Records Numbering Config / Per Group Sequence. Use separate station/group sequences. This changes numbering, not record visibility.
Records Search Config / Index Narrative. Include unprotected narrative in search. Advanced Data Protection enrollment withdraws narrative indexing; this preference cannot override protection.
Records Search Config / Include Legacy History. Include supported legacy personnel and unit logs in the Records search scope. Source permissions still apply.
Records Retention Policy / Department Default Years. Department retention for standard record classes. Zero means permanent; protected classes, prior policy and holds can retain records longer.
Records Retention Policy / Overrides. Definition-specific prospective retention overrides. Use the Records workflow and its confirmations; Admin Assist never purges records.
Records Retention Policy / Last Changed By User ID. Recorded policy-change actor. It is not an editable retention rule and is not exposed as raw identity in this reference.
Records Retention Policy / Last Changed On. Policy effective timestamp used with prior policy versions. It is not the record's retention expiry date.
Records Retention Policy / History. Prior policy versions retained by the owning lifecycle so current changes do not silently rewrite historical retention.
Records Retention Override / Definition Key. Stable record-definition key to which this override applies. Display names do not identify a retention policy.
Records Retention Override / Retention Years. Years retained under this definition override; zero means permanent. Holds and prospective policy resolution still apply.
Records Retention Override / Applies From. Prospective boundary for revisions eligible for the override, evaluated by the Records lifecycle.
Records Retention Policy Version / Effective On. Effective timestamp of a stored historical retention policy version.
Records Retention Policy Version / Policy. Historical policy snapshot used to resolve retention for older revisions. Never edit this as an ordinary preference.
Records Disclosure Config / Statutory Clock Days. Configured disclosure review clock. Verify local obligations with the responsible owner; the default does not establish a legal deadline.
Records Disclosure Config / Default Redaction Profile. Default redaction profile in the owning disclosure workflow. Review the actual proposed release before approval.
Records Disclosure Config / Release Approver User ID. Authorized member responsible for disclosure release approval. Selecting an approver does not grant missing permissions or protected-data access.
Business Operations availability. Controls availability of business operations. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.
Stripe Customer Id. Billing-provider customer reference managed by subscription workflows; never edit this as an ordinary department setting.
Brain Tree Customer Id. Legacy billing reference. Use the subscription provider workflow, not a direct settings edit.
Paddle Customer Id. Billing-provider customer reference. Managed by authorized billing flows and never returned in assistant evidence.
AI availability. Controls availability of optional AI assistance. Disabling this module can remove navigation and block module operations; it does not delete its records. Turning it on still requires the applicable subscription, rollout and permissions.